


VirtualCISOleadershipforcompaniesthatrefusetobethenextheadline.
24/7 managed security and audit-ready compliance for mid-market teams in healthcare, financial services, manufacturing, and SaaS. Fortune 500 protection at a fraction of the cost.


What we do
Senior security practice. Full coverage.
Strategic leadership and deep technical execution under one roof. Talk to a real CISO about which services fit your business.
Virtual CISO
Strategic security leadership without the full-time hire. Risk programs, board reporting, and security roadmaps from someone who's actually run them at Fortune 100 scale.
ExploreSecurity Assessments
From a quick posture read to a full gap analysis and compliance-readiness review, our assessments show you where you stand and the prioritized next steps, board-ready. The clearest first step.
ExploreRegulatory Compliance
SOC 2, HIPAA, CMMC, FedRAMP: turned from blockers into deal-closers. Audit-ready programs in months, not years.
ExploreThreat Operations
Incident response, threat hunting, and forensics from operators who have run real investigations, not playbook readers.
ExploreSecurity Architecture
Zero-trust frameworks, cloud security design, and foundations that scale with your business, not against it.
ExplorePenetration Testing
We think like attackers. Real adversarial testing across applications, APIs, and infrastructure, not automated scans dressed as a report.
ExploreAI Governance
Risk frameworks, regulatory compliance, and responsible AI adoption programs for organizations deploying AI at scale.
ExploreManaged Security
24/7 threat detection, response, and remediation. Eyes on your environment around the clock, with a senior CISO on call when things actually matter.
ExploreSecurity rarely fails for lack of a plan. It fails in the gap between the plan and the people who have to run it.
A strategy no one executes leaves the risk exactly where it was. Tools with no owner get pointed at the wrong problems. In practice, that gap looks like this:
A prospect sends a SOC 2 questionnaire, and nobody actually owns the answer.
A framework sits on the roadmap for a year with no one running the program behind it.
The tool stack keeps growing while the risk it was bought to close never does.
Why BlueRadius
Built by the people who have to run it.
We have run security where getting it wrong was not an option: at Fortune 100 scale, and inside growth-stage teams that inherited the whole problem overnight.
The same pattern showed up every time. No shortage of advice, no shortage of tools, and no one senior actually closing the loop. BlueRadius is the practice those teams needed. Radius360 is the platform we built to run it.
Two ways to work with us
Strategy, and the platform to run it, from one team.
Services
Fractional security leadership
Virtual CISO leadership, managed security, and audit-ready compliance, run by senior practitioners who have done it at Fortune 100 scale.
Explore servicesPlatform
Radius360
The security program platform we build on: it turns your signals into decisions with the evidence attached, across 30 frameworks.
Explore Radius360Not sure where you stand?
Request a security gap assessmentTechnology partners
We deploy and manage industry-leading security platforms across every engagement.


Field reports
What clients tell us.
SOC 2 Type II
8 months. Zero findings.
"Getting SOC 2 certified is a marathon, most companies take over a year. BlueRadius got us there in eight months. We passed our first audit with zero findings. That certification opened doors to enterprise clients we couldn't touch before."
CTO
Data Analytics Startup
A security program
they actually understand.
"What sets BlueRadius apart is they don't just advise, they execute. They embedded with our team, trained our engineers, and left us with a security program we actually understand and can maintain."
Director of Engineering
SaaS Platform
The difference
Why BlueRadius.
Most security firms sell tools or paperwork. We sell judgment, earned over a career of running programs that had to actually hold up.
Senior practitioner, not a vendor
Strategic decisions made by someone who has actually run security programs at Fortune 100 scale. Not delegated to a junior analyst.
We execute, not just advise
We don't hand you a PDF and disappear. We build your security program, train your team, and stay until it works.
Security as business advantage
Compliance and risk management become competitive advantages that win deals, not just internal cost centers.
Outcomes, not deliverables
Measured by what changes for your business. Not by the number of policies generated or screenshots collected.
Leadership
Built by people who've done it.
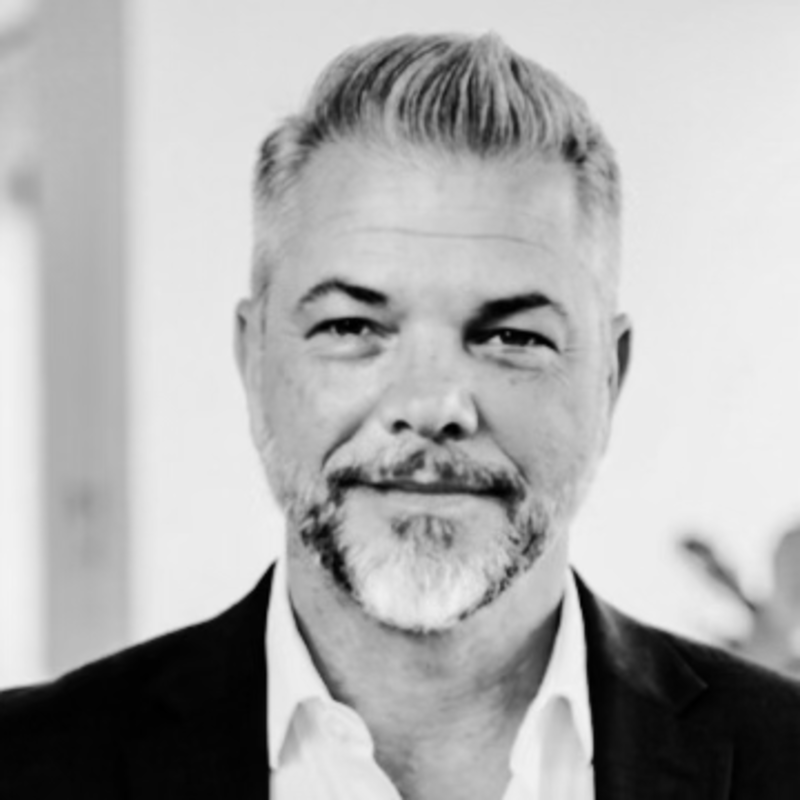
Jeff Sowell
Founder & CEO
CISSP · M.S. · Veteran · Former CISO
"I built BlueRadius because I was tired of watching companies treat security like a checkbox. Real protection takes leadership, not playbooks."
Former Head of Product Security at Ericsson. Built security programs for Microsoft, L'Oréal, and the U.S. Department of Health and Human Services. Twenty years of running real programs and briefing real boards.
Connect on LinkedIn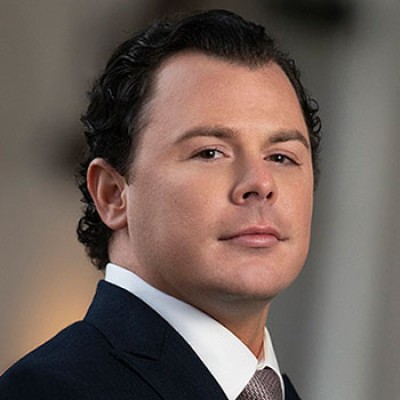
Matthew Hedger
Advisory Board Member
Former CIA · NSA · USN Veteran
"Real-world security isn't about playbooks. It's about judgment, knowing when the rules apply and when they don't."
Partner and Chief Consultant at Busoni Global. Former CIA Operations Officer and NSA cryptologist. Led intelligence operations through deep-cover missions and high-stakes investigations.
Connect on LinkedIn
Aaron Long
VP Security Operations / vCISO
CISSP · M.S. · 15+ Years
Builds and runs the operational engine. SOCs, MDR programs, and security teams that scale across hundreds of client environments.
Former VP of Operations at OneAxiom and SOC Manager at ZeroFox. Senior consultant for Continent8 Technologies in gaming and hospitality. Fifteen years building and scaling SOCs and MDR programs.
Connect on LinkedInGet in touch
Ready when you are.
No pitch deck. No runaround. A direct conversation with a senior practitioner about what you actually need.
Or send a message