AI Coding Agents Have a Software Supply Chain, Too
A practical checklist for tracking tool versions, permissions and changes after approval. How to inventory MCP servers and coding-agent plugins, verify provenance, scope permissions and reopen approval when they change.
Oct 27, 2026
The AI Agent That Writes Its Own Audit Trail Is an Incident Waiting to Happen
An AI agent's own summary can't be the incident record. How to reconcile agent traces with authorization decisions, destination receipts and human approvals, and test it with a forged-record exercise.
Oct 26, 2026
The AI Agents You Didn't Approve Are Already Logged In
Personal AI agents, AI built into the software you already pay for, and agents your teams wired up themselves are connecting to company systems without a security decision. Anthropic's own disclosure shows why that matters, and here is what to do in 30 days.
Oct 14, 2026
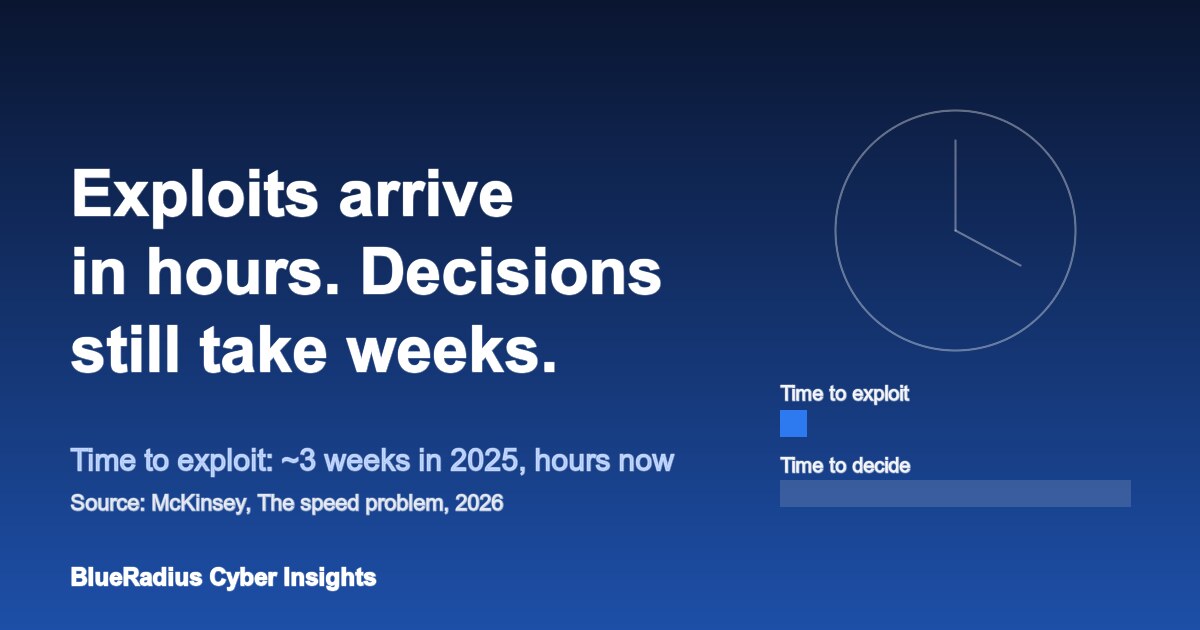
Exploits Now Arrive in Hours. Your Approval Chain Still Takes Weeks.
McKinsey research finds the gap between disclosure and active exploitation of critical vulnerabilities has shrunk from about three weeks to a matter of hours. The slowest part of most responses is no longer the technology. It is deciding who can act.
Oct 12, 2026
ISO 42001 vs NIST AI RMF vs SOC 2 (2026): What Buyers Ask For
Enterprise customers added an AI section to the security questionnaire. Here is what ISO 42001, the NIST AI RMF and SOC 2 each deliver, who issues them, what they cost, and which one your buyers will actually accept.
Oct 5, 2026
Slopsquatting: When AI Coding Tools Invent Your Next Dependency
AI coding assistants routinely recommend software packages that do not exist. Attackers register those invented names and fill them with malware. Here is how slopsquatting works, why the data says it is not a fringe risk, and how to keep it out of your build.
Sep 20, 2026
Securing AI Agents: An Agentic AI Security Guide for 2026
AI agents do not just generate text, they take actions: calling APIs, moving money, changing systems. Here is the agentic AI attack surface and a practical control set for deploying agents safely in 2026.
Jun 17, 2026
NIST AI Risk Management Framework: A 2026 Implementation Guide
The NIST AI Risk Management Framework (NIST AI 100-1) is the de facto US baseline for managing AI risk. This guide covers the four core functions, the Generative AI Profile (NIST AI 600-1), the April 2026 Critical Infrastructure profile, crosswalks to ISO 42001 and the EU AI Act, and a practical adoption path for mid-market organizations.
Jun 1, 2026
AI Cybersecurity Incident Report 2026: The Defining Incidents, Statistics, and Regulations of 2025-2026
The definitive record of AI security in 2025-2026: four zero-click prompt injection chains, the Salesloft Drift breach of 700+ organizations, the first autonomous-agent breach, $893M in FBI-reported AI-enabled fraud, and the corrected EU AI Act timeline. Sourced and footnoted for mid-market leaders.
May 24, 2026
Shadow AI: The Biggest Security Risk Your Company Isn't Tracking
Your employees are already using AI tools you don't know about. Shadow AI is the fastest-growing security risk for mid-market companies.
Apr 5, 2026
AI Vendor Risk Assessment: Questions Your CISO Should Be Asking
Most companies are adopting AI tools without formal vendor assessment. Here's the framework and specific questions your security leader should be asking.
Apr 4, 2026
How to Build an AI Risk Management Program Without a Dedicated Team
Most mid-market companies don't have dedicated AI risk teams. Here's how to build an effective AI risk management program with the resources you already have.
Apr 3, 2026
EU AI Act Compliance: What US Companies Need to Know
The EU AI Act applies to US companies that serve European markets. Here's what mid-market leaders need to know about compliance obligations, timelines, and risk.
Apr 2, 2026
AI Governance Checklist for Mid-Market Companies (2026)
A practical, step-by-step AI governance checklist built for mid-market companies that need to manage AI risk without a dedicated governance team.
Apr 1, 2026
Bay Area AI Security & Governance: Protecting ML Models and Training Data
Bay Area AI companies face unique security challenges: protecting training data, securing ML pipelines, and meeting emerging AI governance requirements. Here's what you need to know.
Mar 26, 2026
Enterprise Product Security in the Age of Claude Code: What Security Leaders Must Do Now
Claude Code is entering enterprise codebases fast. See the 2026 security playbook: repo access controls, secret hygiene, and the controls CISOs need.
Feb 22, 2026
GitHub Copilot Security Review: Complete Guide for Development Firms (2025)
Seven security risks of GitHub Copilot at enterprise scale: code provenance, training-data exposure, secrets leakage, license risk, and controls.
Oct 23, 2025
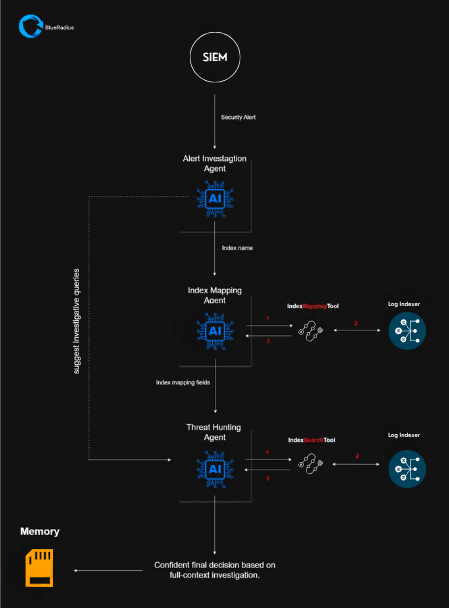
Proactive Threat Hunting with AI-Powered BlueRadius Threat Ops
Move beyond alert fatigue. See how AI-powered threat hunting finds and stops attacks before they cause damage.
Aug 3, 2025
AI-Enhanced Network Security: A Comprehensive Guide
How AI strengthens network security: faster threat detection, automated response, and smarter defense against evolving cyberattacks.
Oct 4, 2024