Attestation Is Not Evidence: Closing the Continuous-Proof Gap
A signed control claim is not proof the control was working the day you were breached. Why point-in-time attestation leaves a gap, and what continuous evidence looks like in a real program.
Sep 20, 2026
ISO 27001 vs SOC 2: Which Compliance Framework Does Your Company Need? (2026)
ISO 27001 vs SOC 2: one is an international certification, the other a US attestation, and they share a large control core. Here is how to choose, and whether to pursue both.
Jun 21, 2026
PCI DSS 4.0.1 Compliance: A Mid-Market Guide for 2026
PCI DSS 4.0.1 is now the only active version of the standard. Here is what mid-market companies that accept card payments need to know: merchant levels, SAQ selection, the 12 requirements, and a readiness checklist.
Jun 17, 2026
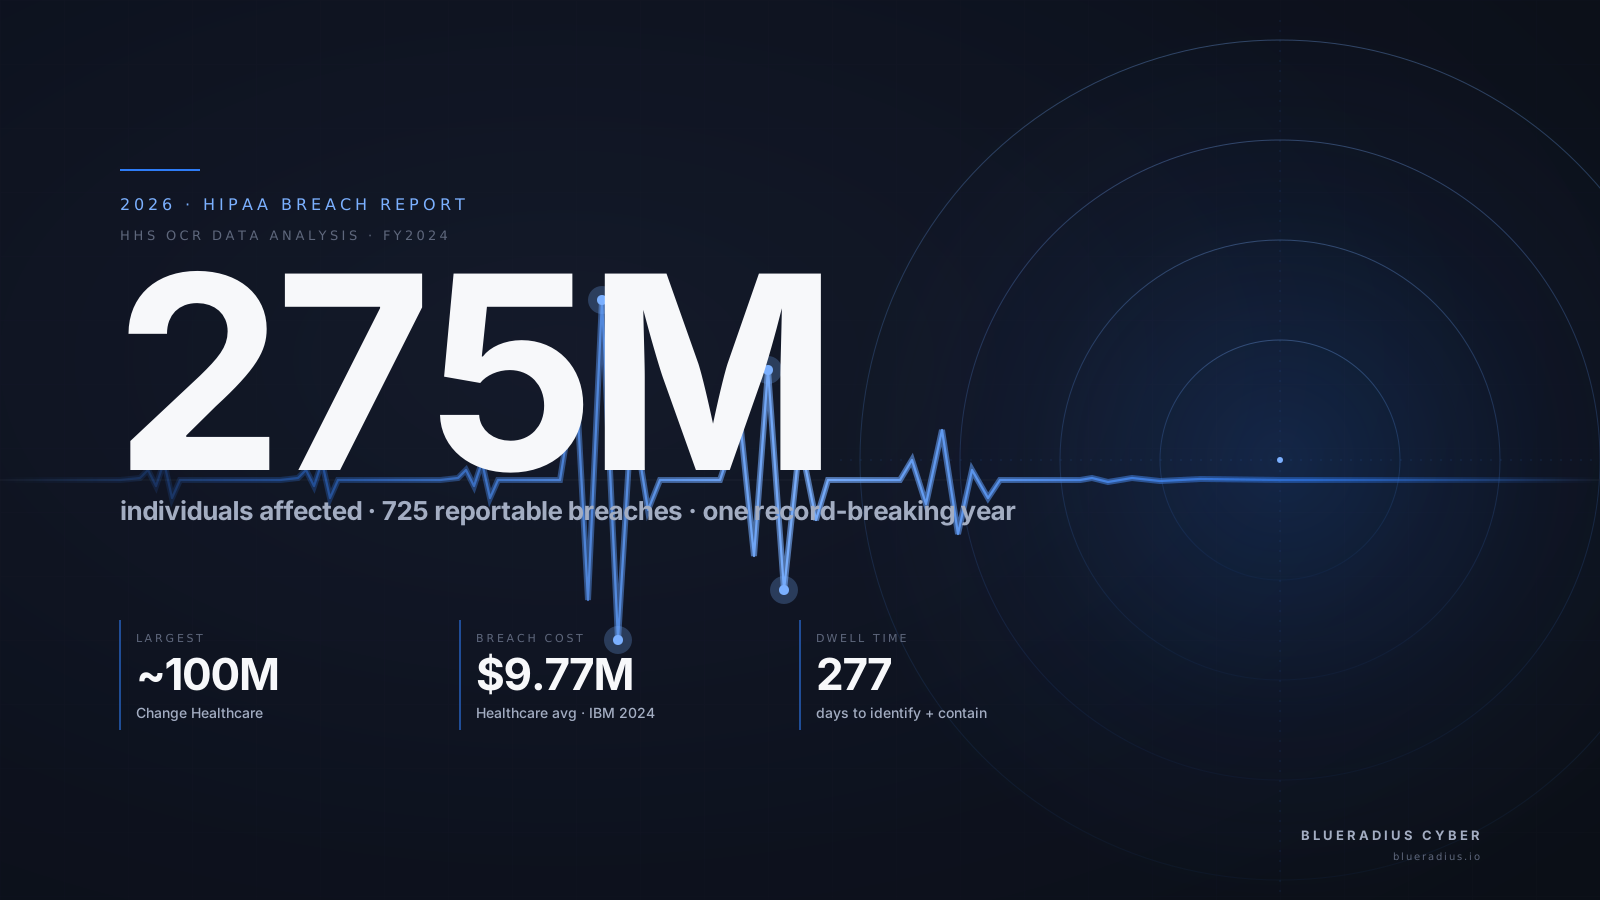
HIPAA Breach Report 2026: OCR Data, Ransomware Trends, and What Mid-Market Healthcare Must Do Next
275 million Americans had their PHI exposed in 2024 — a new HIPAA breach record. Here's what the OCR data shows about ransomware, business associates, and what mid-market healthcare must do next.
Apr 19, 2026
SEC Cybersecurity Disclosure Rules: What Mid-Market Companies Need to Know in 2026
The SEC cybersecurity disclosure rules are reshaping how companies report breaches. Even if you are not publicly traded, these rules affect your business. Here is what mid-market organizations need to do now.
Apr 13, 2026
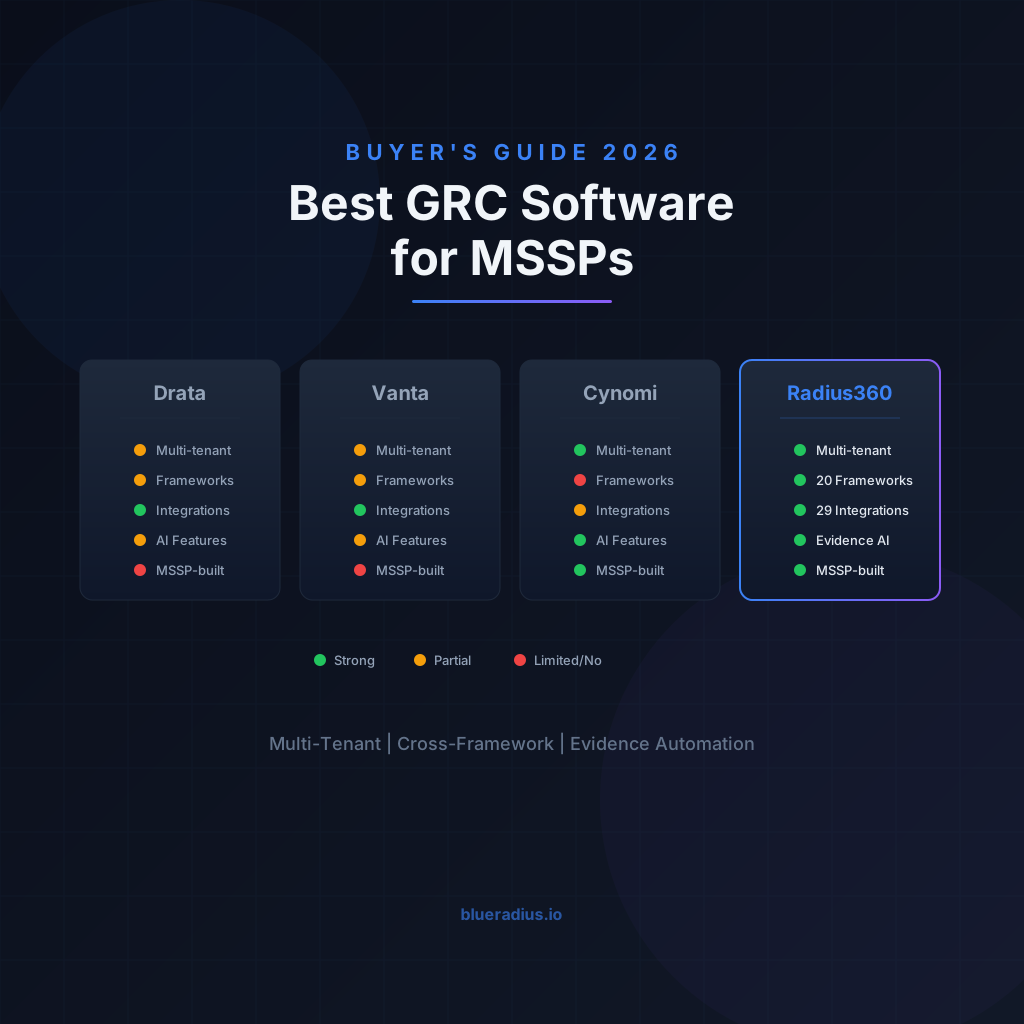
Best GRC Software for MSSPs in 2026: A Buyer's Guide
MSSPs and vCISOs need GRC tools built for multi-client operations — not enterprise platforms shoehorned into service-provider workflows. Here's what to look for in 2026.
Apr 9, 2026
McLean FedRAMP Compliance Services: Authorization for Government Cloud
McLean-area technology companies serving federal agencies need FedRAMP authorization. Navigate the complex authorization process with expert compliance guidance.
Mar 26, 2026
San Diego Defense Contractor CMMC Compliance: A Complete Guide
San Diego defense contractors must achieve CMMC compliance to maintain DoD contracts. Learn the specific controls, timelines, and strategies for certification success.
Mar 26, 2026
Cleveland Supply Chain Cybersecurity Compliance: Protecting Vendor Networks
Cleveland's interconnected supply chains create cascading cyber risk. Learn how to assess vendor security, meet compliance requirements, and protect your organization from third-party breaches.
Mar 26, 2026
What is SOC 2 Compliance? The 2025 Executive Guide
If you're a B2B technology company, chances are you've encountered the phrase "SOC 2 compliance" during sales conversations, customer security questionnaires, or contract negotiations. For many business leaders, SOC 2 starts as just another compliance acronym—but it quickly becomes a make-or-break requirement for landing enterprise clients. This comprehensive guide explains everything executives need to know …
Oct 20, 2025
How MSPs & Consultants Add SOC 2 Services Without Hiring GRC Staff
Quick Summary MSPs and independent security consultants can add significant compliance revenue without hiring GRC specialists. What You Need: Revenue Potential: Timeline: 3 months from evaluation to first client delivery Who This Serves: Managed service providers, independent security consultants, fractional CISOs, and boutique consulting firms Introduction Managed service providers and independent security consultants consistently hear …
Oct 18, 2025
ISO 27001 Certification Guide: Complete Implementation Roadmap for US Companies
ISO 27001 Certification Guide: Complete Implementation Roadmap for US Companies Your UK enterprise prospect just sent over their vendor security questionnaire. Among the requirements: ISO 27001 certification. You have SOC 2 Type II—isn't that enough? Not for international business. While SOC 2 opens doors to US enterprise customers, ISO 27001 is the global standard that …
Oct 7, 2025
CMMC 2.0 Compliance Timeline: When Defense Contractors Must Be Certified
The Department of Defense published the final CMMC 2.0 rule on September 10, 2025, effective November 10, 2025. This marks the end of voluntary self-attestation and the beginning of mandatory third-party cybersecurity verification for defense contractors handling sensitive information. The phased implementation runs through 2028, but waiting until your contract explicitly requires CMMC certification is …
Oct 5, 2025
NIST Cybersecurity Framework for Small Business: Practical Implementation Guide 2025
The NIST Cybersecurity Framework 2.0 has become the gold standard for organizational cybersecurity, but most small businesses struggle to understand how this enterprise-focused framework applies to their resource-constrained environments. Released in February 2024, the updated framework now explicitly targets organizations of all sizes, making it more accessible than ever for small businesses seeking practical roadmaps …
Oct 4, 2025
HIPAA Compliance Checklist 2025: Complete Guide for Healthcare Practices
Healthcare practices across the United States face increasing complexity in maintaining HIPAA compliance while delivering quality patient care. The Health Insurance Portability and Accountability Act (HIPAA) requires comprehensive safeguards for protected health information (PHI), with violations carrying penalties ranging from $100 to $50,000 per incident, and potential criminal charges for willful neglect. This comprehensive HIPAA …
Sep 26, 2025
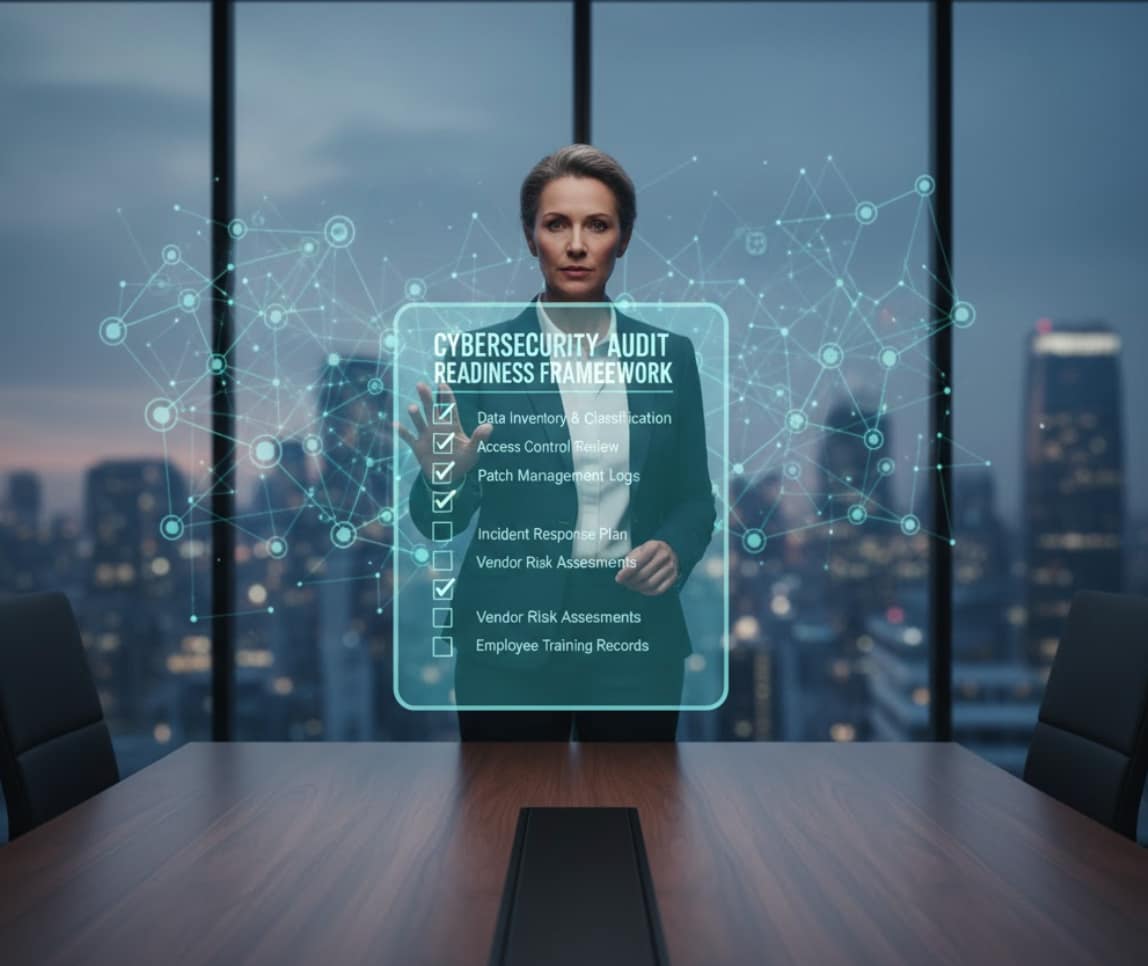
Cybersecurity Audit Preparation Guide: Complete Executive Framework for Business Leaders
Cybersecurity audit preparation is critical for every business that relies on IT systems and digital data. Every system carries some risk, and proper preparation ensures your organization is ready when auditors arrive. A well-executed cybersecurity audit gives leaders a clear picture of vulnerabilities, ensures compliance with industry regulations, and provides actionable steps to strengthen defenses. …
Sep 4, 2025
Cybersecurity Compliance for SMBs: Meeting Regulations Without Losing Focus on Growth
SEO Title: Cybersecurity Compliance for SMBs | HIPAA, SOC 2, CMMC Guide 2025 Meta Description: SMB cybersecurity compliance guide for HIPAA, SOC 2, CMMC & FTC Safeguards. Expert strategies to meet regulations while maintaining business growth in 2025. For many small and mid-sized businesses (SMBs), cybersecurity compliance for SMBs has evolved from an optional consideration …
Aug 31, 2025
Radius360 by Blue Radius Cyber: GRC Without the Headaches
You know what’s really fun? Governance, risk, and compliance (GRC).Said no one ever. If you're reading this, you probably work in cybersecurity—where risk management and compliance don’t exactly come with a gold star for effort. You’ve lived through the endless audit cycles, the paper trail nightmares, and the risk assessments that take longer than the …
Mar 30, 2025
Navigating Compliance with Managed Security Services in Seattle
In the bustling business hub of Seattle, companies are constantly navigating a complex web of regulatory compliance requirements. Whether you’re a startup developing cutting-edge technology or a well-established firm in the finance sector, staying compliant is crucial to avoid hefty fines and reputational damage. Yet, achieving this can be overwhelming and resource-intensive. “Compliance doesn’t have …
Jan 31, 2025